

Federal Agencies Investigate Cyberattacks Targeting U.S. Water Infrastructure
Federal authorities are probing a growing series of cyber intrusions against public water systems in multiple states following warnings regarding foreign threat groups.
By The Global Wire Newsroom · Reported from Michael Casey
Link preview · horizonglobalnews.com
Federal Agencies Investigate Cyberattacks Targeting U.S. Water Infrastructure
Federal authorities are probing a growing series of cyber intrusions against public water systems in multiple states following warnings regarding foreign threat groups.
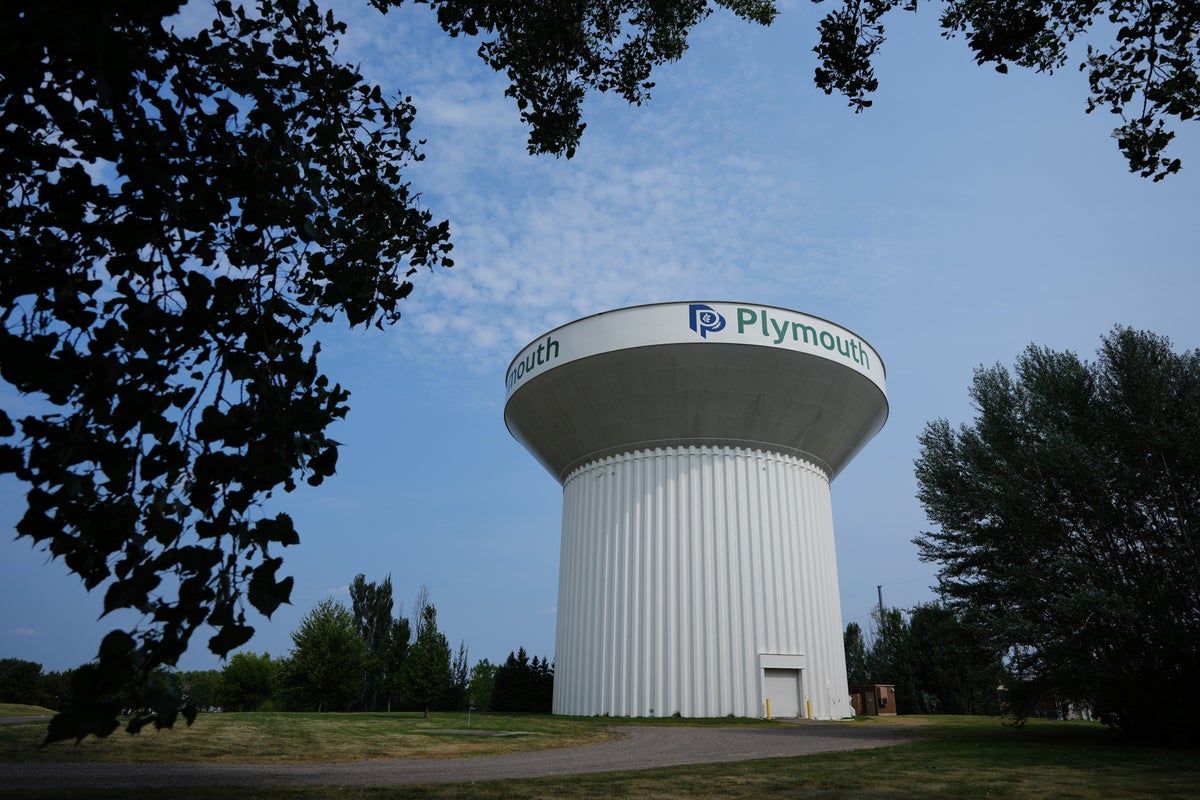
Federal law enforcement agencies are actively investigating an expanding series of cyber incidents targeting public water facilities in several states across the country, according to reporting by Michael Casey.
The Federal Bureau of Investigation continues to examine the intrusions, working to identify the specific entities responsible for penetrating the digital operational networks of domestic water utilities. While federal officials have not formally assigned definitive responsibility for the full scope of recent breaches, the incidents coincide with repeated warnings from U.S. intelligence and cybersecurity agencies regarding Iranian threat actors actively targeting industrial control systems in the public works sector.
Scope of Recent Incidents
The latest wave of cyber activity reflects a growing pattern of digital threats directed at critical national infrastructure, according to reporting by Michael Casey. Public utility operators in multiple jurisdictions have reported unauthorized network access, system disruptions, or scan-and-exploit attempts directed at their operational infrastructure.
When cyber incidents occur within the water sector, the FBI leads the federal government’s criminal and counterintelligence response, coordinating with the Cybersecurity and Infrastructure Security Agency to perform digital forensics, analyze attack vectors, and help affected utilities isolate compromised systems. The primary goal of these ongoing investigations is to determine whether the intrusions represent coordinated campaigns by state-sponsored cyber espionage units or independent opportunistic actors attempting to exploit known vulnerabilities.
Threats to Operational Technology
Water and wastewater treatment facilities rely heavily on industrial control systems, including Supervisory Control and Data Acquisition systems and Programmable Logic Controllers, to monitor and manage physical operations. These automated systems control critical processes such as chemical treatment levels, water pressure management, valve positions, and distribution pumping.
Unlike conventional IT networks that process administrative data and financial transactions, Operational Technology directly manages physical infrastructure. A compromise of these systems can allow unauthorized operators to alter chemical dosing routines, disable pumps, or obscure administrative control screens. Historically, many water systems relied on physical isolation from external networks to prevent unauthorized access. However, as utilities modernise, many have connected their operational technology directly to internet-facing portals or remote monitoring software to permit off-site administrative access, inadvertently exposing control devices to global scanning networks.
Foreign Cyber Activity and Tactical Context
The ongoing FBI investigation follows a period of heightened official concern regarding foreign threat actors, specifically Iranian state-sponsored cyber groups. Federal cybersecurity advisories issued over recent months have highlighted concerted campaigns by advanced persistent threat groups affiliated with Iran’s Islamic Revolutionary Guard Corps targeting critical infrastructure components.
Cybersecurity agencies have noted that Iranian-aligned operators frequently target specific brand-name controllers and industrial devices left accessible over the public internet with weak credentials. In previous advisories, federal authorities warned that threat actors had systematically scanned the internet for exposed human-machine interfaces and industrial control equipment, frequently utilizing default management passwords to alter device displays or disable municipal operations. While investigators have not publicly finalized attribution for every recently impacted utility, the methodologies observed in several recent incidents closely resemble the tactics, techniques, and procedures previously attributed to Iranian groups.
Structural Vulnerabilities in Public Utilities
The U.S. water and wastewater sector comprises roughly 15,000 drinking water systems and 16,000 wastewater treatment facilities, the vast majority of which are managed by local municipal governments or small public utility districts. This extreme fragmentation creates unique defensive challenges across the country.
Many small and medium-sized municipal utilities operate under severe budget constraints and lack dedicated cybersecurity personnel. Operational technology within these facilities is often maintained by plant engineers or third-party contractors who may prioritize system uptime and physical safety over digital security protocols. Consequently, many facilities suffer from common cyber hygiene shortcomings, including unpatched software vulnerabilities, single-factor remote authentication, and legacy equipment that cannot support modern security updates.
Federal Policy and Regulatory Oversight
In response to elevated cyber risks across critical infrastructure sectors, federal regulators and security agencies have sought to enhance cybersecurity mandates for public water systems. The Environmental Protection Agency, which holds primary federal statutory authority over drinking water safety under the Safe Drinking Water Act, has worked alongside CISA to encourage utilities to incorporate cybersecurity evaluations into their mandatory periodic safety assessments.
However, efforts to establish binding federal cybersecurity standards for municipal water facilities have faced regulatory, legal, and operational hurdles. Several state officials and water industry associations have previously challenged federal attempts to mandate specific cyber auditing procedures, arguing that local utilities require federal funding and technical support rather than administrative mandates to achieve compliance. In response, CISA has focused on offering free vulnerability scanning, incident response assistance, and voluntary cybersecurity performance goals tailored to small-scale infrastructure operators.
Defensive Recommendations and Remediation
To protect water networks from ongoing probing and active intrusion attempts, federal cyber defense agencies recommend that public utilities adopt fundamental defense-in-depth strategies. Security guidelines urge operators to perform immediate audits of all internet-facing control devices, disconnect industrial networks from the public internet wherever feasible, and require multi-factor authentication for all remote administrative access.
Furthermore, cybersecurity experts emphasize the importance of retaining manual operational capabilities. By maintaining physical override mechanisms and analog monitoring equipment, plant operators can ensure that safe drinking water standards and baseline distribution functions remain intact even if digital control networks suffer a total loss of availability.
What Comes Next
As the FBI continues its national investigation into the breaches, federal cyber authorities are maintaining active communication with state utility commissions and local water district leadership to disseminate real-time threat intelligence and indicator patterns. Public works departments are being urged to report any anomalous device behavior or unauthorized access attempts immediately to federal response centers.
The expanding scope of these incidents is expected to intensify legislative debates in Washington regarding federal funding for critical infrastructure protection, cyber resilience mandates, and potential technical assistance programs designed to shield local public utilities from sophisticated foreign state cyber threat groups.
This news report is based on original reporting published by Michael Casey.
How this story was produced
This report was written by The Global Wire newsroom from reporting first published by Michael Casey. We verify the core facts against the original report, write our own account, and add the background and consequences a short wire item leaves out. Drafting is AI-assisted inside an editor-supervised pipeline, and every story is checked for accuracy of attribution, structure and duplication before it appears — full detail in our AI and funding disclosure.
Spotted an error? Tell us at corrections@horizonglobalnews.com and read our corrections policy or editorial standards.

Reader comments
Loading comments…